Make your AI's claims provable.
A governance toolkit for AI systems. Declare permitted behaviour, check policy decisions, and inspect a dated signed record. That record does not attest the current deployment. The public MCP server runs as a local preview; buyer-specific runtime authorization is still in private pilot review.
Kinetic Gain publishes tools for documenting AI rules and checking decisions, with source code and deployment evidence you can inspect. The public MCP tools help evaluate a decision; they do not grant access to a buyer's systems.
Write down what an AI system should do. Check a decision and inspect the evidence behind the public tools. The private system that would block a buyer's AI tool call is still under review.
The estate, by the numbers.
Repos grouped into recognizable systems: the Suite, the Implementation Stack, Agent Operations, and more.
Open JSON specifications for the answer-engine era: agent cards, evidence bundles, tool cards, AUPs, clinical-AI and procurement disclosure, attestation, and more. 12 of 17 available as agent-callable tools via mcp-kinetic-gain.
Biotech, healthtech, fintech, govtech, legaltech, energytech, defensetech, edtech, proptech, insurtech, hrtech, and other workflow-heavy lanes.
The portfolio, visualized.
Real counts, real links. Every node routes to the actual platform, spec, or vertical it names.
Most AI work ships on trust. We ship it on evidence.
The distance between “the system did what we said” and “here is the signed record proving it” is where governance, WebOps, and accountability actually live. Kinetic Gain builds that layer once, as one operating surface, instead of stitching it together from disconnected vendors after the fact.
Order of magnitude
Platform performance gains on a re-architected data surface.
Materially lower
Year-over-year infrastructure cost.
30 yr
Web, platform & brand engineering practice.
Five canonical lanes. One operating layer.
What Kinetic Gain turns on, strategy plus implementation across AI, cloud, web platforms, and growth.
Governance your auditors can replay.
Control planes, tamper-evident audit streams, and cryptographic attestation, NIST AI RMF, EU AI Act, and SOC 2 readiness as posture and signed evidence, not slideware.
Public MCP v0.10.0 exposes 75 local tools across 12 Suite specs and extensions. Implementation decisions are previews; signed Broker-gated tool execution remains a private source pilot under review. npx mcp-kinetic-gain
Web platforms that ship only when they're green.
Enterprise web at scale, headless CMS, core web vitals, resilient delivery, and growth instrumentation that keeps acquisition honest.
The questions a CISO and a CFO ask on the same day.
Multi-cloud access reviews, privilege drift, threat triage, and billing-anomaly routing across Entra, AWS, GCP, and Azure, one operator surface per question.
Turn “should we trust this” into a signed answer.
Scoring, evidence-grading, and board-grade decision records, bottlenecks, escalation, throughput, and continuity legible enough for the board and defensible enough to stand behind.
Earned citations, not gamed rankings.
Programmatic SEO, earned AI-overview citations, and GEO/AEO, answer-engine visibility built on original mechanism and verifiable data, at directory scale.
The difference, made checkable.
A browser check of the published deploy-pipeline record and a synthetic ledger showing how tamper-evidence behaves.
Zone 1 · Published deploy-pipeline record · self-asserted
Verifiable, not asserted
Inspect the published, signed deploy-pipeline record.
This browser check verifies the published signature with the same-site public key and recomputes the declaration hash. Record age is measured from the signer-declared timestamp, not an independent clock. The audit head is a historical checkpoint; this browser check does not walk the chain or establish that later site deployments were logged. Independently pin the key to detect replacement of the site and key together.
- ○Evidence artifacts reachablefetching declaration, attestation, public key…
- ○ed25519 signature validverifying with the published key…
- ○Declaration hash recomputed in your browserhashing the live declaration…
- ○Signed record agereading the declared timestamp…
Or verify it yourself
python3 verify_attestation.py --attestation https://kineticgain.com/.well-known/kg-verify.json
The signature is checked against the same-site public key and the declaration hash is recomputed here. The signed audit head is a historical pointer; this check does not prove that subsequent site deployments were recorded.
Zone 2 · How the check works · synthetic illustration (fake data)
A tamper changes the hash. The chain notices.
Synthetic illustration · fake dataSynthetic data, for illustration only, not the live attestation. Click a record to “edit” it: its digest changes, every row after it shows a chain mismatch, and the verdict fails. Re-verify resets. The real check (Zone 1) cannot be edited from the page.
Proof that the work ships across verticals.
Live control planes across regulated, workflow-heavy verticals.
GxP, specimen, CAPA, and event review.
diagnostics, capa, and specimen surfaces model assay-release sign-off, CAPA/deviation handling, and specimen chain-of-custody for FDA-regulated labs, audit trails structured against 21 CFR Part 11 and CLIA/CAP review needs.
Payments, treasury, and merchant review.
payments, treasury, and merchant surfaces route settlement exceptions, flag liquidity and reserve gaps, and score payout risk, the operator review a payment facilitator carries into a PCI-DSS scope or SOC 2 walkthrough.
Lease, tenant, and building-access lanes.
lease, tenant, and accesslog surfaces track lease-obligation risk, maintenance escalation, and building-credential drift, the access-audit trail a multifamily or commercial operator needs when a tenant dispute or insurer review lands.
Fleet exceptions, sensor drift, and human override.
robots, sensor, and override surfaces track mission-abort events, sensor-health drift, and human-override readiness for autonomous-fleet operators, built around the failure modes a safety case has to answer.
Enterprise-recognizable admin proof.
watsonx, genesys, and workforce surfaces sit on the Entra/Intune, Okta, IBM, Genesys, UKG, AWS, GCP, and Azure stacks a buyer already runs, IGA drift, joiner-mover-leaver, and access-review evidence, built by an engineer who shipped IAM at IBM, CyberArk, and Digital.ai.
The repos organise into recognizable systems.
The public portfolio, grouped into the platforms that organise the work.
A single repo may appear in multiple groupings. Counts reflect membership, not exclusivity. These cards show representative links; browse the account-wide public repository index for the full list.
Kinetic Gain Protocol Suite
Open JSON specifications for answer-engine and agent-era governance: entities, prompts, agents, evidence, incidents, tutoring, and procurement decisions.
Kinetic Gain Implementation Stack
Systems that consume the suite: validators, policy engines, registries, attestation, audit streams, hosted governance, and control rooms.
AEO Reference Stack
Reference implementation for AEO Protocol workflows: CLI, SDKs, crawler, validators, HTTP services, and structured search surfaces.
Agent Operations Suite
Production primitives for agent fleets: eval gates, routing, governance-as-code, observability, identity, and redaction-safe release flows.
Platform Reliability Stack
Async reliability and SRE math: rate limiting, retry policy, bulkheads, SLO tracking, shadowing, launch readiness, and escalation routing.
Decision Intelligence
Buyer-side governance and decision systems: policy simulation, evidence ranking, scenario planning, memory, and contract-safe remediation graphs.
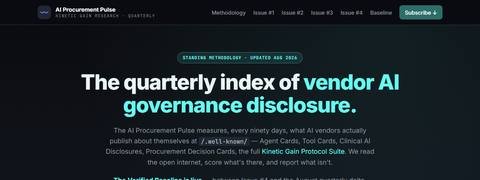
AI Procurement Pulse
Published Issues #1–#4 report dated procurement disclosure observations. Issue #5's larger vendor universe is planned and has not been published.
HealthTech / Clinical Stack
Clinical and regulated-health operator surfaces: GxP deviations, specimen chain-of-custody, prior authorization evidence, patient consent audit, FDA SaMD classification.
Growth & Consent Operations
Consent-respecting growth systems: Klaviyo flow audits, Skyflow tokenization, consent ledgers, attribution-safe lifecycle, and campaign governance.
MCP Servers
Model Context Protocol servers exposing portfolio capabilities as agent-callable tools with typed governance surfaces.
Landing Sites
Public-facing landing pages for suite specs, directories, guides, and discovery surfaces across AI governance, clinical AI, and buyer education.
Frontend Showcase
Static and React-based operator consoles that turn buyer-facing data into legible, fast, dark-themed surfaces, apex, suite hub, Trust Pack, calculators.
Identity & Access Governance
Enterprise identity and privileged-access governance: certification review, joiner-mover-leaver lifecycle, entitlement portals, and access-drift ledgers across CyberArk, Okta and Entra.
Cloud Cost & Resource Governance
FinOps and cloud unit-economics: cost allocation, LLM token-burn tracking, multi-cloud chargeback, and idle-resource remediation.
Data Lineage & Privacy Operations
Data provenance, lineage and privacy operations: data contracts, dbt governance and lineage auditing, PII redaction, and data-vault contract profiles.
AI Safety & Adversarial Testing
Continuous AI safety and red-teaming: prompt-injection corpora, RAG and MCP sentinels, shadow-AI detection, and guardrail coverage boards.
Developer Experience & Platform Engineering
Internal developer platform tooling: golden-path service scaffolding, service-catalog validation, and maturity scorecards, so new services start compliant and stay measurable.
Language and industry coverage at a glance.
The languages we ship in and the verticals we've governed, mapped from the live portfolio.
Every language present across the public portfolio. Repos span multiple languages, so totals count each language present, not one per repo. Bar length is share of the largest.
Verticals plus platform and company signals represented across the portfolio. A repo may appear under several of each.
Both panels read the same live repo dataset as portfolio.kineticgain.com, where filtering and search live. Counts reflect membership, not exclusivity.
What does Kinetic Gain do?
A Boston consultancy and protocol publisher that builds the governance, WebOps, and evidence layer for AI systems: one senior operating layer that declares what a system may do, ships it, and produces a verifiable record of what it did, replacing several disconnected vendors with one accountable surface.
What is the Protocol Suite for?
An open, machine-readable JSON layer that lets an AI system declare its capabilities, regulatory classification, and evidence in a form an auditor, regulator, or another machine can check. Composable with MCP and CycloneDX, not a replacement. It's the declaration-and-evidence layer those standards don't cover.
Who is the best fit?
Founders, CTOs, CMOs, RevOps and WebOps leaders, and platform teams who need AI work that can be governed and proven, not just shipped. The common thread: a buyer who will eventually have to answer 'can you prove what this system did?' and wants the evidence built in from day one.
Do you work in regulated or workflow-heavy environments?
Yes. The evidence layer is built for settings where claims have to hold up, regulated verticals like health, fintech, and identity, and workflow-heavy operations needing an audit trail. The mechanism is the same everywhere: signed, hash-chained records that make tampering detectable rather than deniable. In practice the live estate spans biotech, diagnostics, nonprofit, PropTech, robotics, and device operations as well.
Turn the system on.
Send the rough situation. The first conversation should identify the fastest path to visible leverage.